Curated coverage and comprehensive guides by Fresh Picks.
First, I need to write an original article for the keyword "Auth". The context provided includes various snippets about authentication, session vs token-based auth, Auth0, and some political references that seem unrelated. I'll focus on the authentication topic since that's the primary keyword.
The article should be 600 to 900 words, with natural headings, avoiding unsupported claims, and not mentioning AI generation. I need to return safe HTML using tags like h2, h3, p, ul, ol, li, strong, em.
I'll structure the article around authentication (Auth) concepts. The context mentions "Learn the difference between session and token-based" and "Auth0 is" and "Better", so I can discuss different authentication methods and best practices.
Outline:
- Introduction: Importance of authentication in web applications.
- H2: Understanding Authentication (Auth)
- Definition and role.
- H3: Session-Based Authentication
- How it works, pros and cons.
- H3: Token-Based Authentication
- How it works, including JWT, pros and cons.
- H2: Comparing Session and Token-Based Auth
- Key differences and use cases.
- H3: Modern Approaches: Auth0 and OAuth
- Mention Auth0 as a solution.
- H2: Best Practices for Implementing Auth
- Tips like using HTTPS, secure storage, etc.
- Conclusion: Emphasis on choosing the right method.
I'll incorporate the context subtly. For example, the link about becoming a senior software engineer can be included as a resource without being salesy. But since the requirements say "avoid unsupported claims", I'll keep it informational.
The political context seems irrelevant, so I'll ignore that part.
Now, write the article in HTML format.
Start with the article content.
Note: The user said "Return only safe HTML", so no markdown fences, just raw HTML.
I'll write in plain text with HTML tags.
Article:
The Fundamentals of Authentication in Modern Web Development
Authentication, often abbreviated as Auth, is the process of verifying the identity of a user or system. It is a cornerstone of web security, ensuring that only authorized individuals gain access to resources. In today's digital landscape, understanding different authentication methods is crucial for developers aiming to build secure and scalable applications.
What is Authentication?
At its core, authentication answers the question, "Who are you?" It typically involves credentials like usernames and passwords, but has evolved to include multi-factor authentication, biometrics, and token-based systems. Proper authentication prevents unauthorized access and protects sensitive data.
Session-Based Authentication
Session-based authentication is a traditional method where the server creates a session for the user after successful login. The session ID is stored in a cookie on the client-side and sent with each request. The server then looks up the session data to verify the user.
How it works: User logs in, server creates a session, stores session ID in a cookie, and validates it on each request.
Pros: Simple to implement for server-rendered applications, stateful management on the server.
Cons: Can be less scalable due to server-side storage requirements, vulnerable to CSRF attacks if not handled properly.
Token-Based Authentication
Token-based authentication, on the other hand, is stateless. The user receives a token (e.g., JWT) upon login, which is stored client-side and sent with requests. The server validates the token without storing session data.
How it works: User logs in, server issues a token, client sends it in headers, server decrypts and validates it.
Pros: Highly scalable, suitable for APIs and mobile apps, reduces server memory usage.
Cons: Token management (expiration, revocation) can be complex, secure storage needed to prevent XSS theft.
Session vs. Token-Based Auth: Key Differences
The main difference lies in state
Relevant Guides
Authentication Explained: When to Use Basic, Bearer, OAuth2, JWT & SSO
Become a senior software engineer with a job guarantee: https://go.hayksimonyan.com/126-
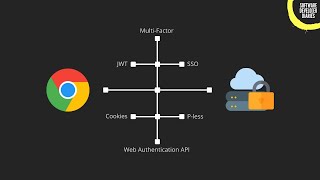
7 Authentication Concepts Every Developer Should Know
Become a senior software engineer with a job guarantee: https://go.hayksimonyan.com/156-
The State of Authentication
Auth
Auth.js Explained
A quick look at
An Illustrated Guide to OAuth and OpenID Connect
OAuth 2.0 and OpenID Connect (OIDC) are internet standards that enable one application to access data from another.